
CRITICALCampaignOct 23, 2026
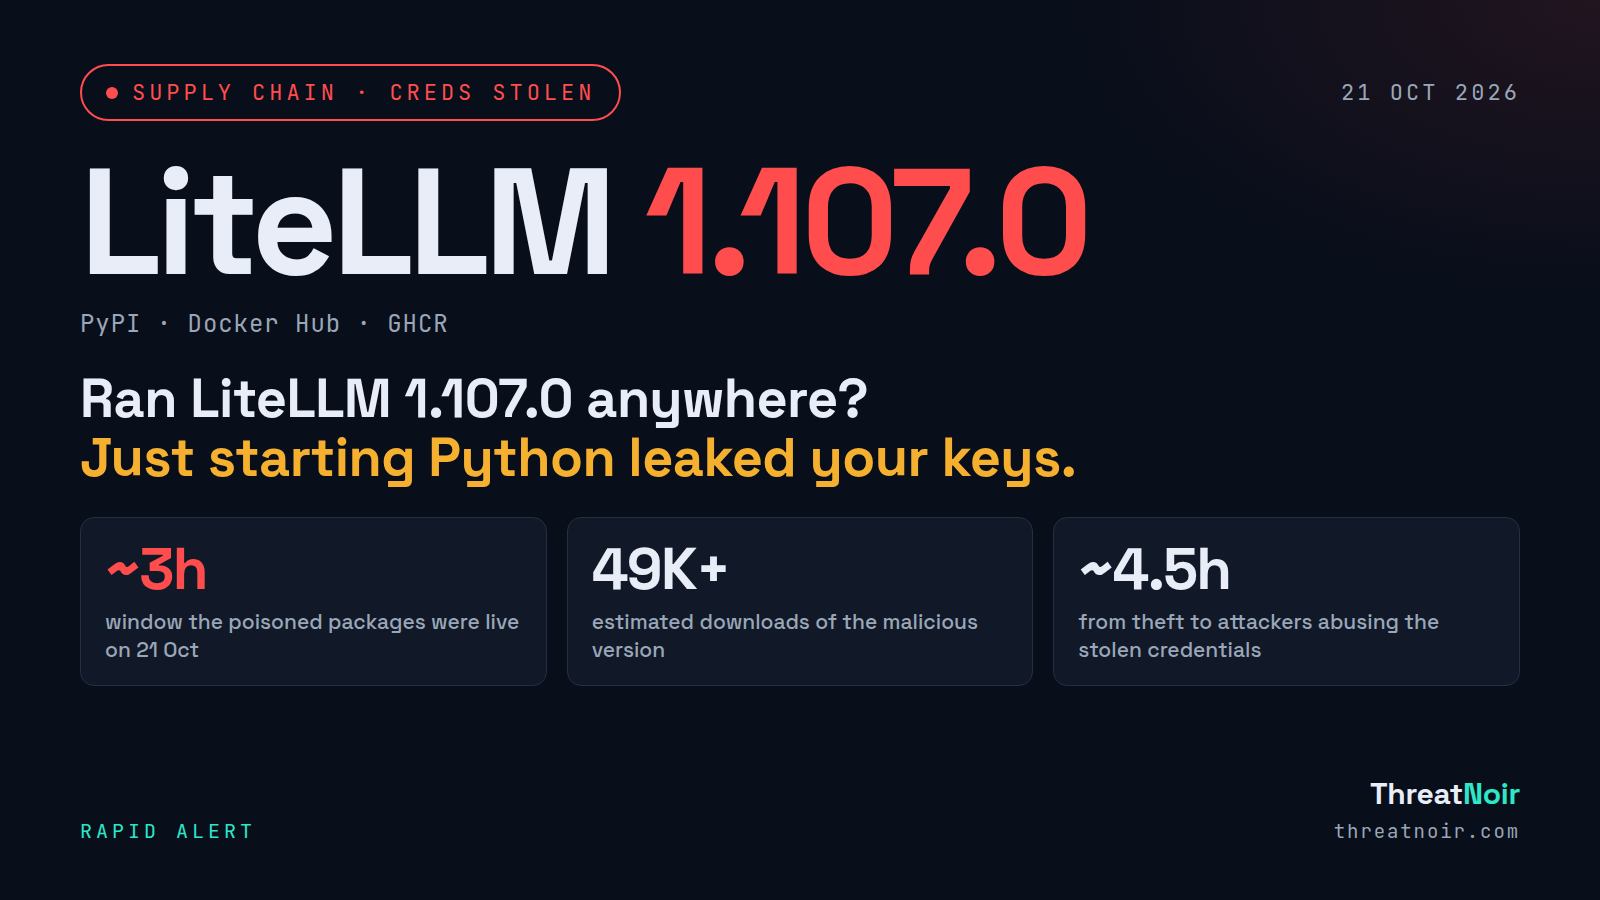
Rapid alert
What to do now: the commands, how to hunt for it and what does not help →
Action required
Deleting the package is not enough. Hooks and an hourly loader survive. Isolate, rebuild clean, rotate every secret.
Affected products
LiteLLM 1.107.0
Linked articles
- LiteLLM Compromised in Fresh Supply Chain Attack
- LiteLLM PyPI Package and Docker Images Compromised to Steal Cloud and AI Credentials
- LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor
- LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
- LiteLLM release pipeline hacked to distribute info-stealer malware