Rapid alert27 October 20263 min read
Gheist campaign abuses stolen GitHub tokens to dump private repo and cloud secrets via Actions logs
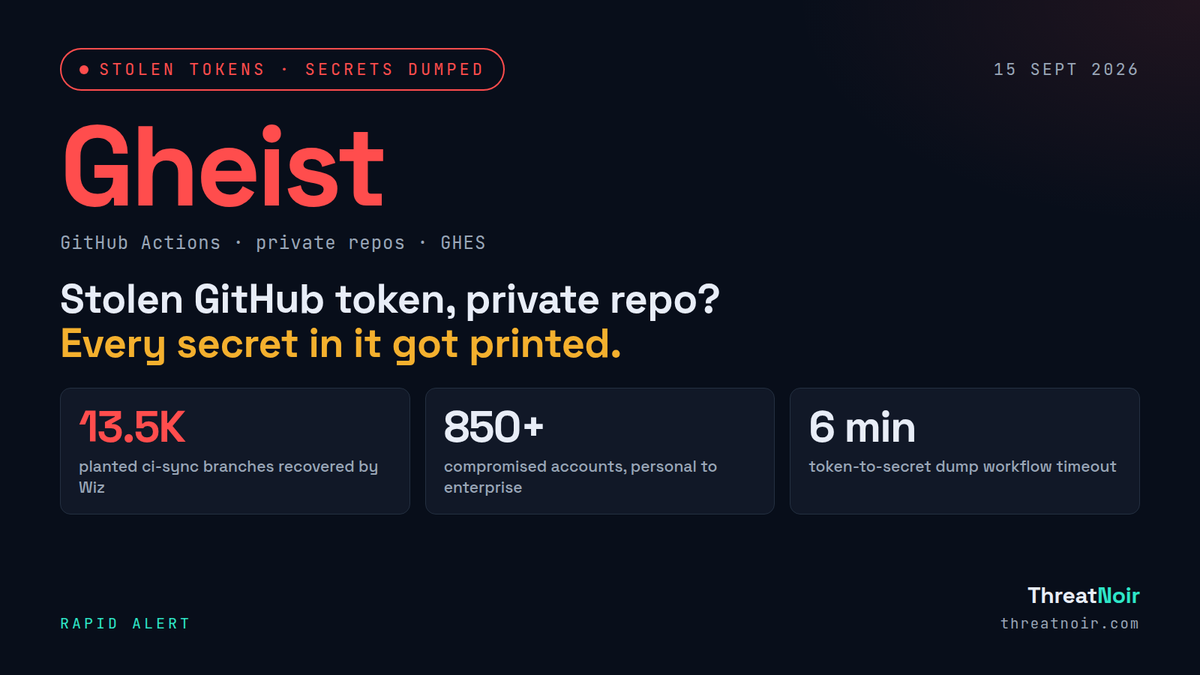
Since 15 Sep 2026, the Gheist campaign has planted a sync-check workflow in over 13,500 branches using stolen GitHub tokens, printing secrets to Actions logs and pulling them before deleting the run. Public repos are protected by a GitHub hold, but private repos and GitHub Enterprise Server are not.
Marcus Lenngren